
Ubiquiti Unifi Security Appliance
4.5Editor score
Three Gigabit Ethernet ports
Integrated Unifi Controller support
VLAN, VPN, and QoS
Explore the 10 best firewall appliances for homes, small businesses, and branch offices, with expert comparisons of ports, throughput, security, and management.
Firewall appliances provide a dedicated barrier between trusted devices and untrusted networks, combining routing, threat protection, VPN support, and centralized controls in one enclosure. The right unit depends on network size, port count, available throughput, administration preferences, and whether you want a vendor-managed platform or a flexible software-loaded system.
This guide compares ten firewall appliances across important considerations including processor performance, Ethernet connectivity, security capabilities, physical design, and deployment requirements. It includes compact mini PCs designed for open-source firewalls, commercial appliances from Fortinet and SonicWall, a Ubiquiti option, and a Palo Alto model, so readers can compare different approaches without relying on unsupported testing claims.
Each entry explains the standout strengths, practical limitations, and ideal operating environment for the product. Ratings reflect the supplied customer feedback, while technical details come from the available product information. Pricing, features, subscriptions, and availability can change, so readers should verify current listing details before making a final purchase.
4.5Editor score

4.6Editor score

4.7Editor score
The comparison below places all ten appliances side by side, emphasizing port configuration, performance, security platform, and administration model. Hardware-only models may require separate subscriptions, while software-loaded mini PCs give administrators greater control over the firewall operating system.



The Protectli Vault FW4B is a compact, fanless firewall micro appliance built around an Intel J3160 quad-core processor. It carries a 4.6 customer rating, and its most compelling qualities are the four Gigabit Ethernet ports, AES-NI support, 8GB of RAM, and a 120GB mSATA SSD. Unlike a conventional router with a fixed configuration, it behaves as dedicated mini-PC hardware that can run the firewall platform selected by the administrator.
We may earn a commission when you buy through this link, at no additional cost to you.
Its four-port layout offers meaningful flexibility for a home, small office, or branch connection. Administrators can assign separate interfaces for a WAN connection, trusted LAN, management network, or additional service without resorting to an external switch. The J3160 can operate at up to 2.2GHz and includes hardware AES-NI support, which is valuable for encryption-heavy workloads such as VPN traffic and encrypted web filtering. Two USB 3.0 ports, two HDMI connectors, and an RJ-45 serial console round out the physical feature set.
The principal trade-off is that no operating system comes preinstalled. Protectli states that the hardware has been tested with pfSense, Untangle, OPNsense, and other popular open-source solutions, giving buyers several established paths. However, buyers must still select, install, configure, and maintain the software themselves. Optional coreboot BIOS support must also be installed by the user, so this is a better fit for a technically confident buyer than someone expecting a turnkey enterprise appliance.
Overall, the FW4B is the strongest all-around recommendation for an administrator who wants capable firewall hardware without paying for a proprietary subscription-based platform. It balances processing power, memory, storage, quiet operation, and four physical network ports in a compact enclosure. It is particularly appealing for those who already understand pfSense or OPNsense and want full control over the operating system and routing configuration.
Four Intel Gigabit Ethernet ports provide enough connectivity for a modest network with separated WAN, LAN, management, and service segments. This makes the FW4B practical for home labs, professional offices, and branch gateways where future interface requirements may differ from the initial setup.
The fanless enclosure keeps the appliance silent while its quad-core processor and AES-NI support provide useful capacity for routing, VPN, and firewall functions. A 120GB mSATA SSD and 8GB of RAM also provide a comfortable foundation for software-loaded gateway workloads.
We may earn a commission when you buy through this link, at no additional cost to you.
The FortiGate-60F is a high-density commercial firewall with ten Gigabit Ethernet RJ45 ports and a 4.4 customer rating. Its standout advantage is the unusually large port count for a compact appliance, including two WAN ports, one DMZ port, and seven internal ports. The security platform also provides purpose-built acceleration, SSL inspection capabilities, SD-WAN functions, and management through Fortinet's broader security ecosystem.
We may earn a commission when you buy through this link, at no additional cost to you.
Fortinet specifies up to 1.4 Gbps IPS throughput and 700 Mbps threat-protection throughput. Those figures make the unit more relevant to small and medium business networks than basic home routers, particularly when the goal is to consolidate several internal services without adding a separate multiport switch. SSL inspection is backed by dedicated security processor technology, while the management console provides network automation, visibility, and Zero Touch Integration with Fortinet Security Fabric.
This listing is appliance-only and does not include a subscription. That distinction matters because advanced security services, ongoing threat intelligence, and some support capabilities are typically delivered through FortiGuard and FortiCare offerings. Administrators must determine whether the hardware alone is sufficient for their immediate requirements or whether they will add a security subscription. The device also demands more deliberate configuration than a simple consumer router.
The FortiGate-60F is a strong recommendation for organizations that value port density, established security features, and a unified commercial platform. It is especially useful for branch offices, small enterprises, and managed networks that can make use of dedicated DMZ and multiple internal connections. Buyers seeking a fully activated appliance may also examine the separate FortiGate-60F bundle included in this guide.
The included security processor supports demanding inspection functions, including encrypted traffic analysis and firewall acceleration. Its stated IPS and threat-protection throughput positions it well for small-business gateways that need more capability than a basic home router provides.
Ten Gigabit Ethernet ports eliminate the need to add an external switch for many branch layouts. Separate WAN, DMZ, and internal connections also simplify network segmentation and make the appliance well suited to segmented business infrastructure.
We may earn a commission when you buy through this link, at no additional cost to you.
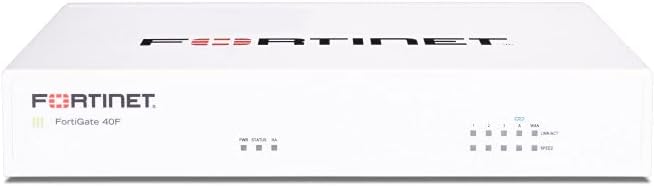
The FortiGate-40F is a compact, fanless desktop firewall designed for small businesses, branch offices, and other modest network environments. Its 4.2 rating reflects an established appliance with a practical five-port configuration. One Gigabit Ethernet port is designated for WAN connectivity, while four internal ports provide enough room for servers, access points, workstations, and management equipment.
We may earn a commission when you buy through this link, at no additional cost to you.
Fortinet lists up to 1 Gbps IPS throughput and 600 Mbps threat-protection throughput. The appliance uses Fortinet's purpose-built security processor to accelerate network operations and protect SSL-encrypted traffic. It also integrates with the AI-powered FortiGuard Labs platform for identifying and mitigating known and unknown threats. The user-oriented management console adds automation and visibility, while Zero Touch Integration with Security Fabric supports more streamlined deployment.
Its main limitation is that this version is sold as appliance only, without a subscription. That makes the listing more useful for administrators who already understand Fortinet licensing or intend to activate the appropriate services separately. The five-port layout is also more restrained than the FortiGate-60F, so networks with numerous wired endpoints may need an external switch. Even so, the dedicated internal ports are more purposeful than the limited interface count of many consumer routers.
The FortiGate-40F is a persuasive option for organizations that want commercial security capabilities in a quiet, space-efficient unit. It works particularly well for a small office or branch endpoint where predictable firewall throughput, clear internal segmentation, and centralized visibility matter. It is less suitable for buyers seeking a fully serviced subscription bundle or a very large number of built-in network interfaces.
Five Gigabit Ethernet ports give a small network one WAN and four internal connections without turning the firewall into an oversized enterprise device. The fanless desktop form also reduces noise and makes placement straightforward.
IPS, encrypted-traffic protection, FortiGuard threat intelligence, and network visibility bring substantial controls to smaller installations. Zero Touch Integration can simplify deployment for teams already using the Fortinet ecosystem.
We may earn a commission when you buy through this link, at no additional cost to you.
The Ubiquiti Unifi Security Appliance is a compact gateway for users who want firewall controls within the Unifi management ecosystem. It has a 4.5 customer rating and offers three Gigabit Ethernet ports, including a management port. Its principal attractions are straightforward Controller integration, VLAN support, enterprise VoIP quality of service, and a built-in VPN server for secure communications.
We may earn a commission when you buy through this link, at no additional cost to you.
The USG is especially attractive to an organization already using Unifi access points, switches, and network management. Rather than introducing a disconnected administration environment, it brings gateway functions into a familiar interface. The device can be mounted on a wall or placed on a desktop, making it easy to position near the center of a small home, office, or retail network. Its three-port design also creates a simple gateway-and-managed-switch arrangement.
The limited port count is the clearest constraint. With one management port and two other Gigabit Ethernet connections, a network with multiple wired clients will probably require a Unifi switch. The appliance also makes the most sense when centralized Ubiquiti management is desirable; a buyer seeking a broader selection of independent firewall operating systems may prefer a mini PC. Nevertheless, VLAN support, QoS, and VPN functions cover several important small-network needs.
The Unifi Security Appliance is our best budget-oriented recommendation for an existing Unifi user because it combines network control and gateway security in one ecosystem. It is especially well suited to small offices, home businesses, and branch networks seeking a tidy, centrally managed deployment without a large enterprise appliance. Its compact construction and approachable feature set outweigh the limited interface count for the right buyer.
Integration with the Unifi Controller allows firewall, access point, and switch administration to fit within the same management environment. That consistency can reduce configuration friction for organizations that have already standardized on Unifi equipment.
VLAN support helps separate network traffic by purpose, while QoS for enterprise VoIP gives voice traffic useful priority. A VPN server adds another common small-office security function without requiring a separate gateway.
We may earn a commission when you buy through this link, at no additional cost to you.
The SonicWall TZ280 is a next-generation firewall with a 4.7 customer rating, the highest rating among the listed products. It stands out for up to 2.5 Gbps firewall inspection throughput, 1 Gbps threat-prevention throughput, and 1.2 Gbps IPSec VPN throughput. Its networking is equally flexible, combining eight 1GbE ports with two 1G SFP connectors in a desktop enclosure.
We may earn a commission when you buy through this link, at no additional cost to you.
SonicOS 8 provides a broad security toolset once the required subscription is active. Listed capabilities include intrusion prevention, gateway anti-malware, application control, TLS and SSL decryption, Capture ATP multi-engine sandboxing, and reputation-based content and DNS filtering. SonicWall's RFDPI engine performs the underlying deep packet inspection work, while the platform also supports secure SD-WAN, IPSec and SSL VPN, and Zero-Trust Network Access through Cloud Secure Edge.
The listing is hardware only. Security services, firmware updates, and support are not included and must be purchased separately, so the total ownership cost depends heavily on the subscription chosen. That makes careful accounting essential. In exchange, the subscription unlocks the active protection features that distinguish a next-generation firewall from a basic packet-filtering gateway. Management is available on-box or through SonicWall's cloud Network Security Manager, with zero-touch deployment support.
The TZ280 is our premium selection for small businesses and branch offices that need comprehensive application control, encrypted-traffic inspection, SD-WAN, and remote-access capabilities. It is a particularly compelling fit for organizations willing to purchase the relevant service subscription. Buyers comparing it with the FortiGate models should assess both the desired security services and the long-term licensing structure before deciding.
SonicOS 8 combines intrusion prevention, anti-malware, application control, encrypted-traffic inspection, sandboxing, and reputation filtering. These tools make the TZ280 more suitable than a basic firewall for organizations that need detailed control over modern application traffic.
Eight copper ports and two SFP connectors support a variety of branch arrangements, including high-speed uplinks. Secure SD-WAN, IPSec and SSL VPN, and zero-trust access broaden the appliance beyond a traditional perimeter gateway.
We may earn a commission when you buy through this link, at no additional cost to you.
The Netgate 1100 pfSense+ is a ready-to-configure security gateway with pfSense+ already installed. It carries a 4.1 customer rating and combines firewall, router, and VPN functions in a compact, low-power enclosure. Unlike a generic mini PC requiring an operating system, it arrives with software preloaded and includes lifetime pfSense+ updates, Netgate TAC Lite support, and a one-year hardware warranty.
We may earn a commission when you buy through this link, at no additional cost to you.
Its dual-core ARM Cortex-A53 processor runs at 1.2GHz and delivers near-gigabit routing for common home iPerf3 traffic. Netgate specifies firewall throughput in excess of 650 Mbps, making the unit suitable for many small office and branch networks. Three switched Gigabit Ethernet ports can be configured as separate WAN, LAN, and optional interfaces, providing enough connectivity for a modest network without a large port array.
The main constraint is port count. Three Gigabit Ethernet connections are sufficient for a basic gateway, but they become restrictive as more access points, servers, or managed switches require dedicated connections. In addition, while pfSense+ software updates are included for the product lifetime, buyers should understand the wider Netgate software ecosystem and understand the terms associated with support beyond the included offering. Delivery also requires an adult signature.
The Netgate 1100 is a strong choice for a buyer who wants the flexibility of the pfSense platform without installing it personally. It is especially useful for technically capable home users, small businesses, and developers who need a dependable firewall, router, and VPN gateway in a quiet appliance. Compared with a bare-metal micro PC, it offers a faster path to operation and more clearly defined support resources.
Preloaded pfSense+ software removes the operating-system installation step from the buying process. The included expert assistance option can also help new owners establish their first secure network configuration.
The dual-core ARM processor and three switched Gigabit Ethernet ports suit compact offices and home networks. Low power draw and silent operation allow the gateway to remain inconspicuous on a desk, wall, or rack.
We may earn a commission when you buy through this link, at no additional cost to you.
The FortiGate-100E is a Fortinet network security appliance with a 4.7 customer rating, tying the highest rating in this group. The supplied information highlights its ability to protect against known exploits, malware, and malicious websites while detecting unknown attacks and identifying thousands of applications. That combination places it squarely in the category of business-focused next-generation security appliances.
We may earn a commission when you buy through this link, at no additional cost to you.
Application identification is particularly relevant in modern networks where users connect to services that may not fit neatly into traditional port-based categories. Likewise, protection against malicious websites and malware provides a practical layer beyond basic firewall rules. The ability to detect unknown attacks signals a more comprehensive security model than a simple packet-filtering device, while the FortiGate platform gives administrators a path toward centralized network visibility.
The available product data is brief, so buyers should carefully verify the exact port configuration, throughput ratings, included accessories, and current subscription terms. It would not be responsible to infer detailed specifications that are not stated in the supplied information. The appliance may also require appropriate FortiGuard or support services for some security capabilities, making the final configuration an important part of the purchasing decision.
The FortiGate-100E is a strong candidate for organizations already invested in Fortinet's security ecosystem. Its high customer rating and stated application awareness make it appealing for branch offices and small-to-medium networks seeking a dedicated commercial firewall. Prospective buyers should compare its verified current specifications against the more fully documented FortiGate-40F and FortiGate-60F alternatives before making a final selection.
Identifying thousands of applications gives administrators more context than basic source and destination rules. This visibility supports tighter policies for business networks where different services carry different levels of risk.
The FortiGate platform is designed for more than basic packet filtering, with stated defenses for exploits, malware, malicious sites, and unknown attacks. Teams already using Fortinet products may benefit from a consistent management approach.
We may earn a commission when you buy through this link, at no additional cost to you.
The Palo Alto PA-220 is an eight-port next-generation firewall security appliance offered as a new-condition product. Its 3.0 customer rating is the lowest among the ten options, so it should be evaluated with particular care rather than treated as an automatic choice. The product belongs to a well-known enterprise firewall family, and its defining listed characteristic is an eight-port appliance format.
We may earn a commission when you buy through this link, at no additional cost to you.
Eight ports can provide a useful balance for a branch firewall, where several internal services or network segments need direct connections. The next-generation firewall designation indicates that Palo Alto positions the device for modern application-aware security rather than only basic address and port filtering. For organizations that already standardize on Palo Alto products, continuity of platform and operating practices may be a meaningful advantage.
The supplied listing provides almost no detailed specifications, performance figures, interface types, or subscription terms. As a result, buyers should verify throughput, supported protocols, management options, and the condition and contents of the unit before purchase. A lower customer rating can reflect the specific listing experience, but it is still a legitimate warning that warrants additional research. Subscription requirements should also be confirmed because managed security features commonly depend on active support and threat-intelligence services.
The PA-220 may suit a branch or technical organization that values the Palo Alto platform and needs an eight-port physical layout. It is not the most obvious choice based on the available evidence alone, because the limited listing data make direct comparison harder. Buyers should use it when platform consistency is essential, and should compare it carefully with the better-documented Fortinet, SonicWall, Ubiquiti, and Protectli options.
Eight physical ports give the appliance more wired flexibility than the most compact gateways in the guide. That makes it potentially useful for branch networks that must connect several internal systems while maintaining a dedicated perimeter role.
Organizations already using Palo Alto security systems may value a consistent approach to policy management and threat inspection. Verifying current licensing and specifications is essential because the supplied product listing provides limited detail.
We may earn a commission when you buy through this link, at no additional cost to you.
The Protectli Vault FW4C is a compact firewall mini PC distinguished by four Intel 2.5 Gigabit Ethernet ports. It has a 4.5 customer rating and uses an Intel J3710 Pentium quad-core processor with four threads, running at 1.6GHz and bursting to 2.6GHz. AES-NI hardware support is included, making the appliance relevant to networks where encrypted workloads and VPN services require efficient processing.
We may earn a commission when you buy through this link, at no additional cost to you.
The 2.5G interfaces are the FW4C's defining feature. They can accommodate faster internal links than standard Gigabit Ethernet while retaining four dedicated ports for WAN, LAN, management, and service networks. The enclosure is fanless and silent, and its physical connectors include two USB 3.0 ports, two HDMI outputs, and an RJ-45 serial port. It is therefore also suitable as a compact administration system rather than only a gateway appliance.
The specifications are more modest than those of the Protectli Vault FW4B. Memory is 4GB of DDR3 rather than 8GB, and storage is a 32GB SSD rather than a 120GB mSATA drive. As with the FW4B, no operating system is preinstalled, and the buyer must install the desired platform. Protectli reports compatibility with pfSense, Untangle, OPNsense, and other popular open-source firewall software after hardware testing.
The FW4C is a good fit for a buyer who prioritizes multi-gigabit networking over maximum memory or storage. It can serve a compact home, small office, lab, or branch point where 2.5G links are already available or anticipated. For broader software flexibility, heavier customization, or extensive local storage, the FW4B deserves a closer look.
Four 2.5GbE ports provide substantially more link headroom than standard Gigabit interfaces. The addition can benefit modern switches, servers, and storage systems while maintaining a compact firewall footprint.
Intel AES-NI support helps the J3710 handle encryption efficiently, an important consideration for VPN and encrypted traffic inspection. The four-thread processor also provides a capable base for compact gateway workloads.
We may earn a commission when you buy through this link, at no additional cost to you.
The FortiGate-60F bundle combines the FortiGate-60F network security appliance with one year of FortiGuard Unified Threat Protection and FortiCare Premium. It holds a 4.2 customer rating and is aimed at medium-sized businesses that want meaningful protection without building the infrastructure of a much larger enterprise. The bundle provides an initial period of security services and support around a high-density firewall platform.
We may earn a commission when you buy through this link, at no additional cost to you.
Unified Threat Protection is designed to address advanced online threats using comprehensive web filtering and anti-botnet technologies. FortiCare Premium adds customer support and service continuity during the included term. Together, these elements address a common problem with hardware-only appliances: the device may be installed correctly, yet active threat intelligence and support still need to be purchased. Including them initially reduces that gap for the first year.
The important consideration is renewal planning. The bundle covers one year, while continued protection will require attention when that period ends. Buyers should compare the renewal structure with the cost of using the separate FortiGate-60F appliance-only listing, particularly if they already hold other Fortinet services. As with other FortiGate deployments, actual network segmentation, policy design, and application usage determine how much benefit the organization receives.
This is the most straightforward choice in the guide for a business that wants both the FortiGate-60F hardware and its security services at the outset. The ten-port design provides extensive connectivity, while the first year of UTP and FortiCare Premium reduces initial configuration friction. It is a strong option for a medium business or branch that values a packaged commercial security deployment and can plan for ongoing service renewal.
Bundling UTP and FortiCare Premium gives the buyer an initial year of web filtering, anti-botnet protections, and premium support. This is more complete than acquiring the appliance alone and leaving essential service decisions for later.
The underlying FortiGate-60F platform provides ten Gigabit Ethernet ports for varied business network layouts. That makes the bundle relevant to organizations needing more interface density than compact three-port gateways can offer.
We may earn a commission when you buy through this link, at no additional cost to you.
Choosing a firewall appliance requires balancing network capacity, security platform, port requirements, management preferences, and ongoing service costs. The best device is the one that fits the intended environment without paying for unused capabilities or accepting a configuration process beyond the buyer's comfort level.
Throughput is the amount of traffic the appliance can process while enforcing its security functions. Raw processor or port speed alone does not guarantee adequate firewall performance, because intrusion prevention, encrypted-traffic inspection, VPN processing, logging, and application control can reduce the rate at which traffic moves. The FortiGate-40F is listed at up to 1 Gbps IPS throughput, while the FortiGate-60F reaches 1.4 Gbps. The SonicWall TZ280 is positioned for up to 2.5 Gbps firewall inspection. Compare these figures with the actual bandwidth of the fastest Internet or uplink that must pass through the device.
Every active Ethernet connection consumes a physical interface unless a separate switch is used. The Netgate 1100 and Ubiquiti Unifi Security Appliance each offer three Gigabit Ethernet ports, which can be limiting in a small office. The Protectli models add four dedicated ports, and the FortiGate-60F provides ten RJ45 connections divided among WAN, DMZ, and internal roles. The SonicWall TZ280 goes further with eight 1GbE ports and two SFP connectors, offering more flexibility for network types and uplink distances. Buyers should count WAN ports, management access, servers, access points, and any future expansion before choosing.
A firewall's capabilities may depend on whether it is a conventional appliance, a software-loaded mini PC, or hardware sold with a limited service period. The FortiGate-60F appliance-only listing and SonicWall TZ280 hardware-only listing require separate security services, firmware, and support arrangements. The FortiGate-60F bundle includes one year of FortiGuard UTP and FortiCare Premium, while the Netgate 1100 includes pfSense+ updates for the product lifetime under the stated terms. Protectli appliances do not include an operating system and allow the administrator to install a supported firewall platform. These models differ greatly in control, convenience, and long-term cost.
Basic firewall rules may be sufficient for a simple network, but modern threats and cloud applications often justify deeper controls. Look for IPS, anti-malware, web filtering, application identification, botnet protection, encrypted-traffic inspection, and DNS filtering according to the risk profile. FortiGuard-based products emphasize broad threat intelligence, while the SonicWall TZ280 lists intrusion prevention, gateway anti-malware, application control, TLS and SSL decryption, sandboxing, and reputation-based filtering. The FortiGate-100E highlights protection against exploits, malware, malicious sites, and unknown attacks, plus application identification. These features may require subscriptions, so the advertised hardware is only the starting point.
Remote work, branch connectivity, and partner access can make VPN performance a deciding feature. The SonicWall TZ280 is specified for up to 1.2 Gbps IPSec VPN throughput and also supports SSL VPN and zero-trust access through Cloud Secure Edge. The Ubiquiti USG includes a VPN server for secure communications, and the Netgate 1100 combines firewall, router, and VPN functions with pfSense+ preinstalled. Buyers should determine whether employees connect through IPsec, SSL, a vendor zero-trust service, or an independently hosted application. Device count and expected simultaneous sessions matter as much as headline VPN speed.
The management platform determines how easily policies can be created, monitored, and maintained. Fortinet appliances use a management console with automation, visibility, and Zero Touch Integration for Fortinet Security Fabric. SonicWall supports on-box management and its cloud Network Security Manager, with zero-touch deployment. Ubiquiti integrates firewall functions with the Unifi Controller, which is convenient for existing Unifi users. Protectli and Netgate provide routes into software-oriented administration, with the former offering operating-system choice and the latter providing a preloaded pfSense+ environment. Consider your team's existing tools and willingness to learn a new interface.
A firewall is normally placed where all traffic must pass, so its size, noise, power use, and mounting options can affect installation. The Protectli Vault FW4B and FW4C are fanless and silent micro appliances, and the Netgate 1100 is designed for low power draw and silent operation. The FortiGate-40F also uses a compact fanless desktop form. The FortiGate-60F and SonicWall TZ280 provide denser interface arrangements that may suit equipment areas. The Ubiquiti USG can be wall mounted or placed on a desk. Choose a layout that leaves room for cables, ventilation, and future servicing.
Firewall ownership extends beyond the initial installation, so support and updates deserve early attention. The Netgate 1100 includes Netgate TAC Lite technical support, free setup help from its Technical Assistance Center, pfSense+ updates for the product lifetime as stated, and a one-year hardware warranty. The FortiGate-60F bundle includes one year of FortiCare Premium, and the SonicWall TZ280's service subscription is explicitly separate from the hardware. Protectli includes US-based support and states that its hardware has been tested with major open-source firewall platforms. Buyers should review support scope, firmware expectations, security-update responsibilities, and replacement intervals.
Begin with a written inventory of the existing network, including the ISP or uplink, router, access points, servers, managed switches, VPN users, VLANs, and planned growth. Decide which device will perform routing, which will provide firewall services, and where each physical interface will connect. Document the purpose of every port before moving cables, and keep a direct management path available in case the new policy blocks remote administration.
Install the required software or activate the relevant security subscription, then apply a minimal working configuration before adding advanced services. Create separate trusted, guest, server, and management networks where appropriate. Enable logging, schedule automatic configuration backups, and test internet access, local services, VPN connections, DNS, and update delivery. For subscription appliances, confirm that threat intelligence, firmware, and support are active rather than assuming the hardware works at full protection immediately.
After deployment, review firewall policies regularly, remove obsolete rules, update passwords and credentials, and monitor logs for denied traffic and unexpected administrative changes. Keep firmware and firewall software current, but schedule major updates carefully and retain a tested recovery path. Check ventilation, cable strain, and indicator status, and avoid placing the appliance where liquids, excessive heat, or direct impact can interfere with operation.
A basic wireless router may provide some firewall functionality, but a dedicated appliance usually offers more control, better visibility, stronger inspection features, and clearer separation between network segments. It can also handle VPN, application control, threat filtering, and centralized logging more effectively. Consider a dedicated firewall when a home has many connected devices or a business needs stronger access control and remote connectivity.
An open-source-loaded mini PC offers broad operating-system choice, ownership over configuration, and no required proprietary platform subscription. A commercial appliance generally provides a more integrated management console, vendor support, threat-intelligence services, and simpler ongoing administration. The better choice depends on technical skill, licensing preferences, and how much control the organization wants to maintain.
Hardware-only appliances provide the physical gateway, but some advanced threat-protection, firmware, intelligence, and support services may require separate purchase. Subscription bundles include selected services for a defined period, often making the initial deployment more complete. Compare the included service term and renewal cost carefully, because the long-term cost can materially change which appliance is the better value.
Three ports may be enough for a minimal network with one WAN, one LAN, and one management or service connection. Four ports offer more separation, while eight or ten are useful when a firewall must connect several internal services, access points, or network segments. If a dedicated switch handles endpoint connections, the firewall still needs enough ports for the WAN, management, and logical networks that must remain physically separated.
Several models explicitly include VPN capabilities. The Netgate 1100 supports VPN through pfSense+, the Ubiquiti USG includes a VPN server, and the SonicWall TZ280 provides IPSec and SSL VPN functions along with zero-trust access. FortiGate models also support secure remote and branch connectivity. Confirm protocol compatibility, user capacity, licensing, and expected throughput before choosing.
The right figure depends on peak traffic and the number of security functions enabled simultaneously. A business with fast broadband or a busy internal network should choose measured firewall or IPS throughput above its expected sustained load. A small home may need much less, while a branch gateway handling encrypted traffic, applications, and VPN sessions should leave considerably more processing headroom.
2.5GbE can be valuable when the network includes fast switches, servers, storage, or a high-speed internal backbone. It offers a middle ground between 1GbE and 10GbE equipment and can support efficient switching in modern homes. If every client and connected device is limited to 1GbE, the faster interfaces may offer little immediate benefit, although they provide future expansion.
Review policies and logs at least periodically and immediately after major network changes, such as new servers, cloud applications, remote offices, or a changed user base. Remove obsolete rules, check for denied administrative attempts, confirm update status, and verify that backups can be restored. Continuous monitoring tools can help identify unusual activity between scheduled reviews.
The Protectli Vault FW4B is the leading overall choice for administrators who want capable, quiet, flexible firewall hardware and the freedom to select their own software. The Ubiquiti Unifi Security Appliance is the practical budget option for existing Unifi users, while the SonicWall TZ280 is the premium selection for organizations seeking extensive next-generation security and branch-connectivity features.
Before buying, prioritize the factors your environment will actually experience: measured throughput, required physical ports, VPN protocol, management expertise, and security-service licensing. A larger appliance is not automatically better, and a subscription is not automatically worthwhile if nobody will configure or use its advanced features. The most effective choice fits the network cleanly and can be maintained over time.
Finally, verify the current product listing, supported software, included services, and subscription terms before ordering. Firewall hardware, licensing, and availability can change, and current details may differ from the information available when this guide was prepared. Checking those details alongside your real bandwidth and port requirements will lead to a more informed final decision.